> For the complete documentation index, see [llms.txt](https://robertos-notebook.gitbook.io/vuldarcourses/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://robertos-notebook.gitbook.io/vuldarcourses/ceh-content/enumeration/module-04-practical.md).

# Module 04 - Practical

Those are the steps that I took to complete the flag-hunting session, in the current module of the CEH v12 Practical Course.

### Flag 1

Name the shared folder/drive available on the Windows Server 2019 machine.

Using Windows 11 machine CMD, type:              nbtstat -c

```bash
nbtstat -c
```

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-1.bmp" alt="" height="76" width="493"><figcaption><p>Screenshot of the output</p></figcaption></figure>

A:                    \\\WINDOWS11\CEH-Tools

### Flag 2

Use the NetBIOS Enumerator to perform NetBIOS enumeration on the network (10.10.1.15 – 10.10.1.100). Enter the domain name associated with the IP address 10.10.1.22.

You can use the tool **netbiosenumerator.exe** from E:\CEH-Tools\CEHv12 Module 04 Enumeration\NetBIOS Enumeration Tools\NetBIOS Enumerator to get the result

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-2.bmp" alt="" height="102" width="413"><figcaption></figcaption></figure>

Or using the Parrot Terminal, the following command:

```bash
nbtstat 10.10.1.22 -vh
```

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-3.bmp" alt="" height="341" width="408"><figcaption><p>nbtscan output</p></figcaption></figure>

A:                    CEH

### Flag 3

Use snmp-check to enumerate a target and find the hostname of the machine at the IP address 10.10.1.22.

```bash
snmp-check 10.10.1.22
```

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-4.bmp" alt="" height="363" width="624"><figcaption><p>snmp-check’s output</p></figcaption></figure>

A:                    Server2022.CEH.com

### Flag 4

What is the domain name of the machine at the IP address 10.10.1.22?

From the previous command `snmp-scheck 10.10.1.22`

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-5.bmp" alt="" height="63" width="624"><figcaption></figcaption></figure>

A:                    CEH

### Flag 5

Enumerate the machine at 10.10.1.22 using snmp-check and find the number of user accounts.

From the previous command `snmp-scheck 10.10.1.22`

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-6.bmp" alt="" height="122" width="134"><figcaption></figcaption></figure>

A:                    6

### Flag 6

Perform SNMP enumeration using **SoftPerfect Network Scanner** and find the hostname of the machine at 10.10.1.9.

Remember to add Host Name at: Options > SNMP Remote

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-7-3.bmp" alt="" height="261" width="624"><figcaption><p>Output from SoftPerfect Network Scanner, tool provided by CEH. Red: Flag 6, Blue: Flag 7, Green: Flag 8</p></figcaption></figure>

A:                    ubuntu.local

### Flag 7

Perform SNMP enumeration using SoftPerfect Network Scanner and find the hostname of the machine at 10.10.1.14.

From the scan image at Flag 6

A:                    Android.local

### Flag 8

Perform SNMP enumeration using SoftPerfect Network Scanner and find the Host Name of the machine at 10.10.1.22.

From the scan image at Flag 6

A:                    Server2022

### Flag 9

Use SnmpWalk to perform SNMP enumeration on the Windows Server 2022 machine. Enter the option that sets a community string.

From the lab documentation:

```bash
snmpwalk -v1 -c public 10.10.1.22
```

* -v         specifies the SNMP version number (1 / 2c / 3)
* -c         sets a community string

A:                    -c

### Flag 10

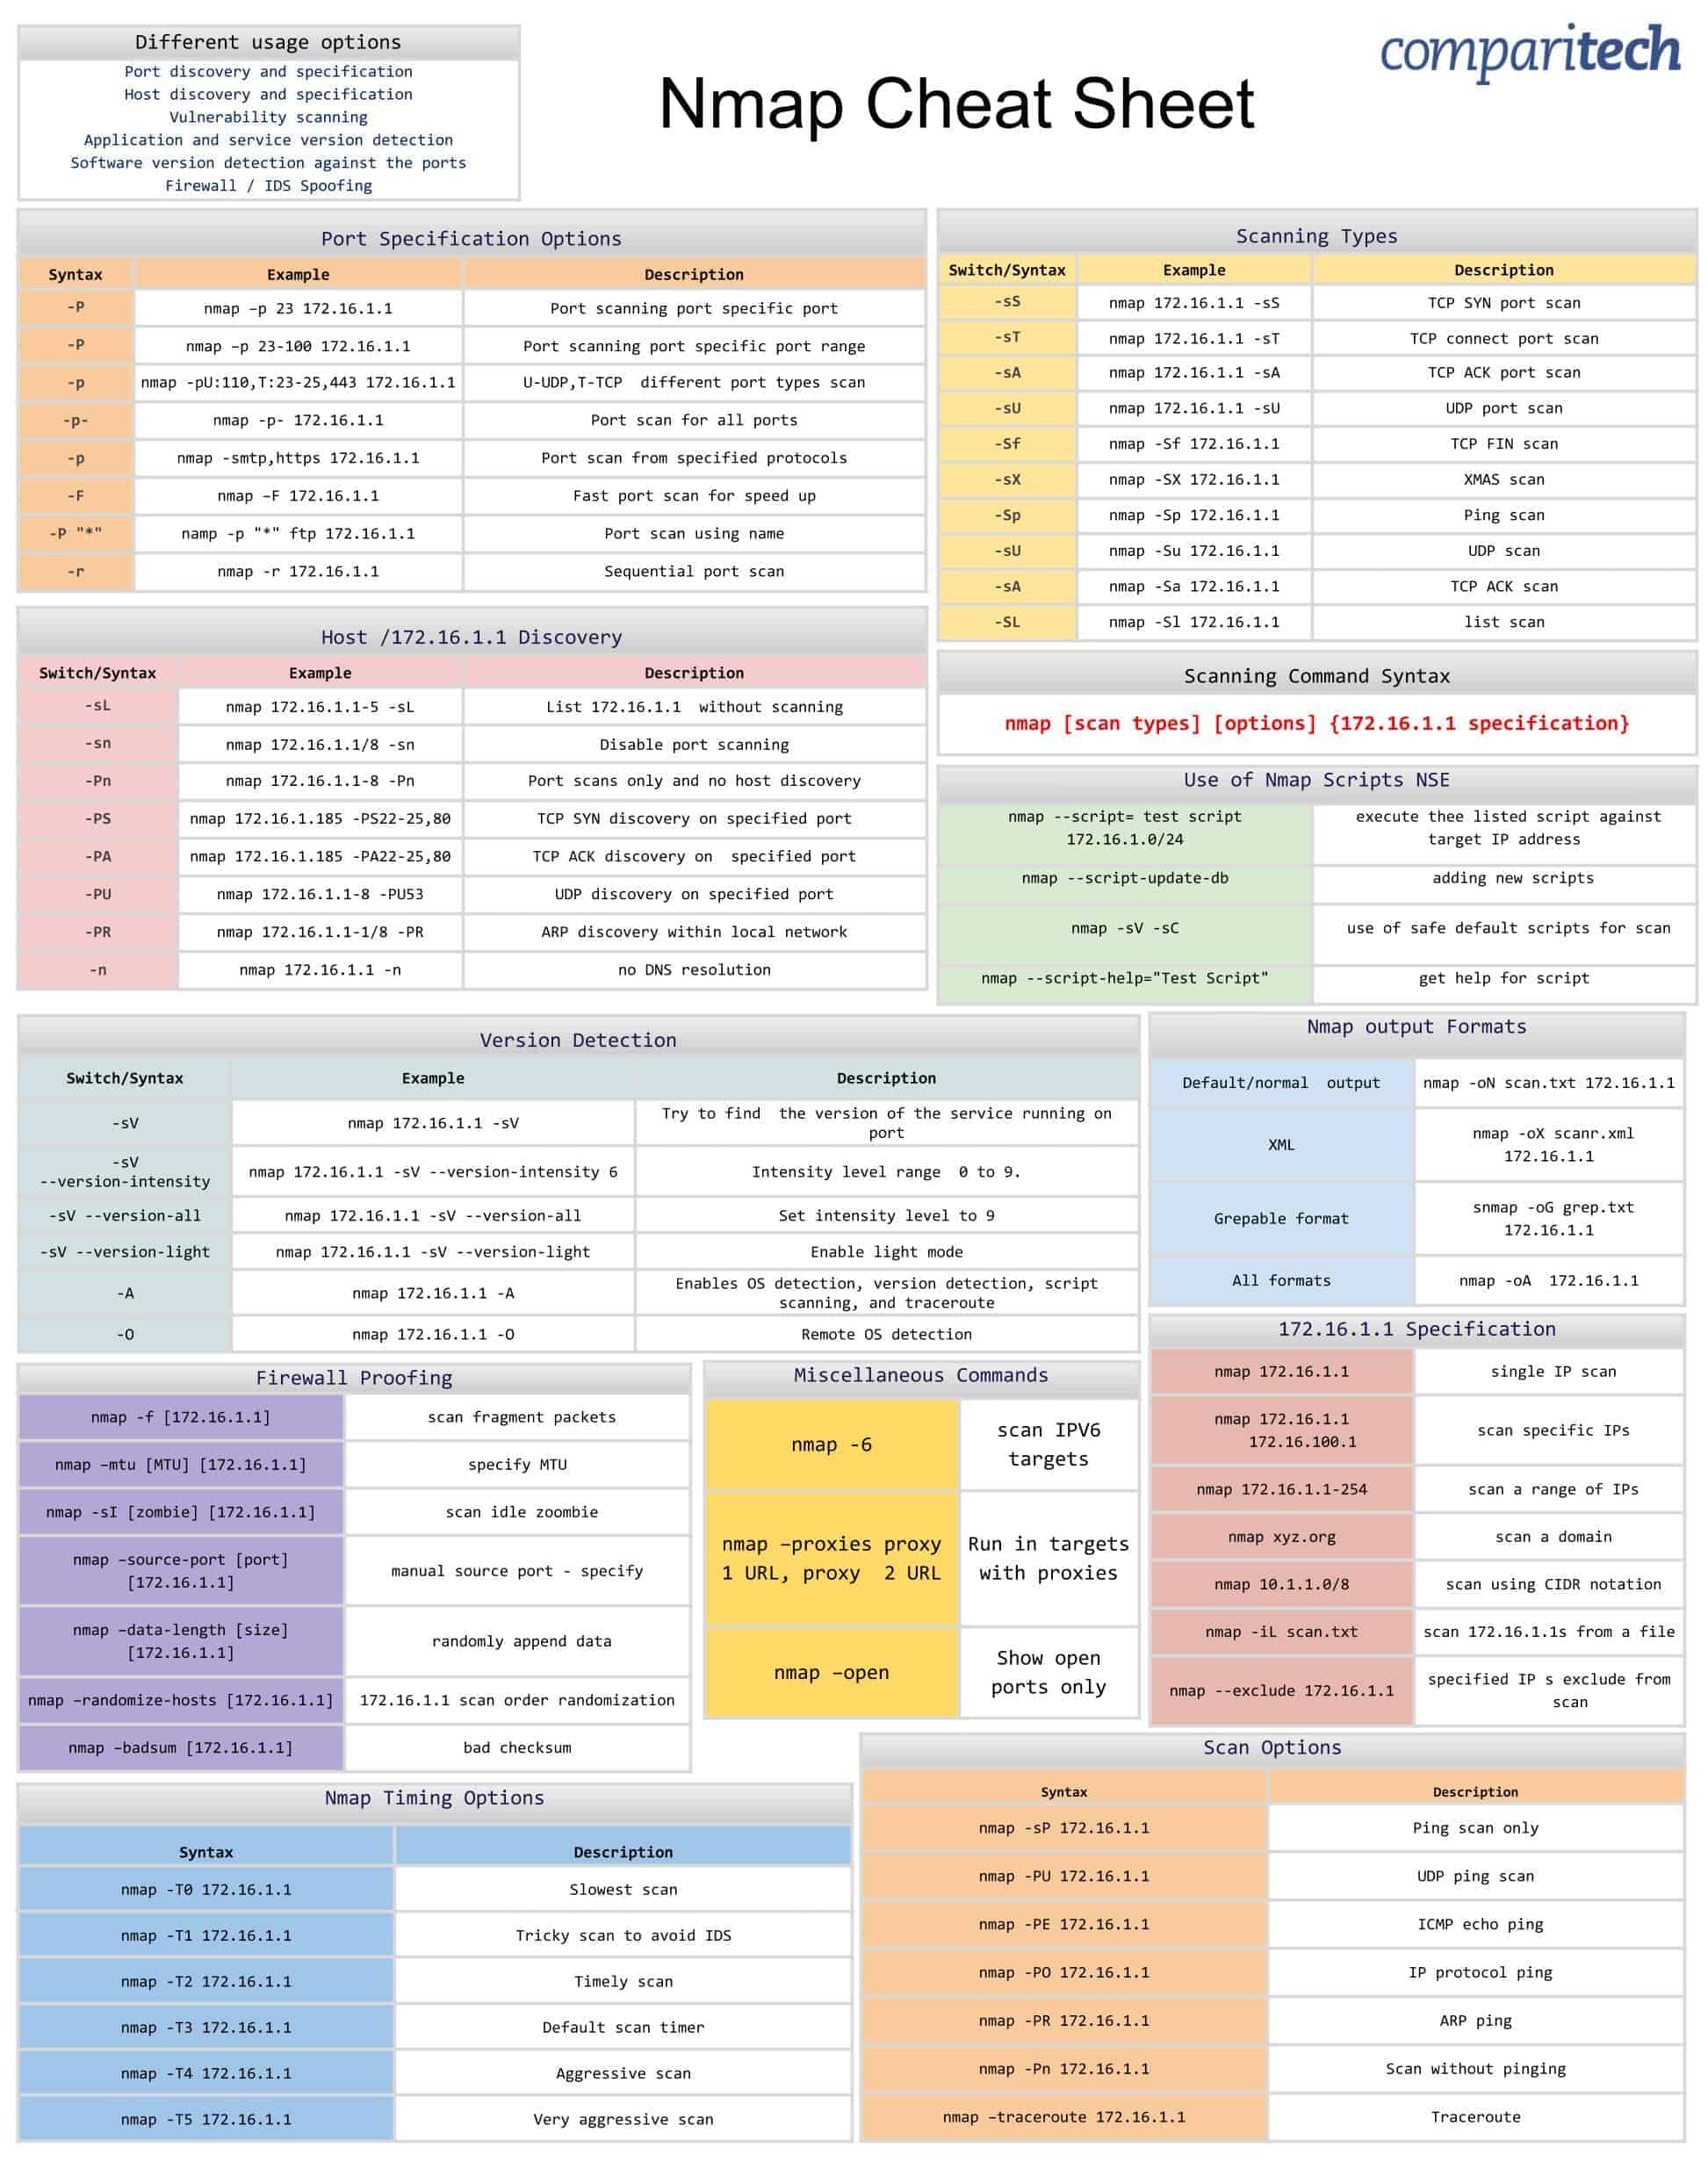
Use various Nmap scripts to perform SNMP enumeration on the Windows Server 2022 machine. What is the option that is used to specify a UDP scan?

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-8-1.bmp" alt="" height="357" width="624"><figcaption><p><a href="https://cdn.comparitech.com/wp-content/uploads/2019/06/Nmap-Cheat-Sheet-1.jpg">https://cdn.comparitech.com/wp-content/uploads/2019/06/Nmap-Cheat-Sheet-1.jpg</a></p></figcaption></figure>

A:                    -sU

### Flag 11

Use various Nmap scripts to perform SNMP enumeration on the Windows Server 2022 machine. Enter the option that specifies the port to be scanned.

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-9-1.bmp" alt="" height="269" width="624"><figcaption><p>From: <a href="https://cdn.comparitech.com/wp-content/uploads/2019/06/Nmap-Cheat-Sheet-1.jpg">https://cdn.comparitech.com/wp-content/uploads/2019/06/Nmap-Cheat-Sheet-1.jpg</a></p></figcaption></figure>

A:                    -p

### Flag 12

Perform LDAP Enumeration using **Active Directory Explorer (AD Explorer)** and find the Domain Controller machine’s IP address.

User:               Administrator

Pass:                Pa$$w0rd

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-10-1.bmp" alt="" height="214" width="520"><figcaption><p>Active Directory Explorer, Windows Tool provided by CEH</p></figcaption></figure>

A:                    10.10.1.22

### Flag 13

Perform LDAP enumeration using **Active Directory Explorer (AD Explorer)** and find the userPrincipalName for the user named Jason.

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-11-1.bmp" alt="" height="147" width="624"><figcaption><p>Active Directory Explorer, Windows Tool provided by CEH</p></figcaption></figure>

A:                    <jason@CEH.com>

### Flag 14

Use Nmap and Python commands to extract details on the LDAP server and connection. Enter the port number that is used by LDAP.

A:                    389

### Flag 15

Use Python commands to extract details on the LDAP server and connection. Enter the command used in python shell to gather information such as naming context or domain name.

```bash
python3
```

Step by step:

```python
import ldap3
server=ldap3.Server(‘10.10.10.25’, get_info=ldap3.ALL,port=389)
connection=ldap3.Connection(server)
connection.bind()
server.info
```

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-12-1.bmp" alt="" height="226" width="558"><figcaption><p>Result from the Python method to get the LDAP server information</p></figcaption></figure>

A:                    server.info

### Flag 16

Use ldapsearch to perform LDAP enumeration on the target system to gather details related to the naming contexts. Which option is used to specify simple authentication?

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-13-1.bmp" alt="" height="259" width="624"><figcaption><p>Information from: https://securitysnake.blog/ldapsearch-cheatsheet/</p></figcaption></figure>

A:                    -x

### Flag 17

Use ldapsearch to perform LDAP enumeration on the target system to obtain more information about the primary domain. Which option is used to specify the base DN for search?

A:                    -b

### Flag 18

Perform NFS Enumeration using RPCScan and SuperEnum and find the port used by the NFS service on 10.10.1.19.

A:                    2049

### Flag 19

Can you perform **zone transfer** on the primary host of certifiedhacker.com? (Yes/No)

{% code title="Parrot Terminal" %}

```bash
dig @ns1.bluehost.com www.certifiedhacker.com axfr
```

{% endcode %}

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-14-1.bmp" alt="" height="92" width="438"><figcaption></figcaption></figure>

A:                    No

### Flag 20

Perform DNS enumeration and find the “responsible mail address” for the domain certifiedhacker.com.

{% code title="Windows Terminal" %}

```bash
$ nslookup
$ set type=cname
$ certifiedhacker.com
```

{% endcode %}

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-15-1.bmp" alt="" height="263" width="576"><figcaption></figcaption></figure>

A:                    dnsadmin.box5331.bluehost.com

### Flag 21

Perform DNS enumeration using **dnsrecon** and find the IP address of the name server (ns2) for certifiedhacker.com.

{% code title="Parrot Terminal" %}

```bash
$ cd /home/attacker/dnsrecon
$ chmod +x ./dnsrecon.py
$ ./dnsrecon.py -d www.certifiedhacker.com
```

{% endcode %}

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-16-2.bmp" alt="" height="292" width="624"><figcaption><p>Output from dnsrecon.py</p></figcaption></figure>

A:                    162.159.25.175

### Flag 22

Use nmap to perform DNS enumeration on certifiedhacker.com to gather the list of all the available DNS services on the target host along with their associated ports. What is the rDNS record for 162.241.216.11?

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-17-1.bmp" alt="" height="328" width="624"><figcaption><p>From the previous code</p></figcaption></figure>

A:                    box5331.bluehost.com

### Flag 23

Use the Nmap to perform SMTP enumeration to enumerate the list of all the possible mail users on the Windows Server 2019 machine. Enter the number of users enumerated on the target machine

{% code title="Parrot Terminal" %}

```bash
nmap -p 25 --script=smtp-enum-users 10.10.1.19
```

{% endcode %}

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-18.bmp" alt="" height="322" width="396"><figcaption><p>Nmap’s Output</p></figcaption></figure>

A:                    10

### Flag 24

Perform SMB enumeration using NetScanTools Pro. Is SMB version 1 (SMB 1) enabled on the machine at 10.10.1.19? (Yes/No)

{% code title="Parrot Terminal" %}

```bash
nmap -p 445 -A 10.10.1.19
```

{% endcode %}

Term:              nmap -p 445 -A 10.10.1.19

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-19.bmp" alt="" height="224" width="587"><figcaption><p>Nmap’s output at SMB</p></figcaption></figure>

A:                    No

### Flag 25

Enumerate the machine at 10.10.1.19 using Nmap and find its http-server-header.

{% code title="Parrot Terminal" %}

```bash
nmap -T4 -A 10.10.1.19
```

{% endcode %}

Try:                 nmap -T4 -A 10.10.1.19

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-20.bmp" alt="" height="227" width="426"><figcaption></figcaption></figure>

A:                    Microsoft-IIS/10.0

### Flag 26

Perform enumeration using Global Network Inventory and find the full name of the OS installed in the machine at 10.10.1.22.

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-21.bmp" alt="" height="332" width="541"><figcaption><p>Output from Global Network Inventory, tool provided by CEH</p></figcaption></figure>

A:                    Microsoft Windows Server 2022 Standard

### Flag 27

Enumerate network resources using Advanced IP Scanner and find the version of the Apache httpd service running on the machine at 10.10.1.9.

{% code title="Parrot Terminal" %}

```bash
nmap -T4 -A 10.10.1.9
```

{% endcode %}

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-22.bmp" alt="" height="220" width="511"><figcaption></figcaption></figure>

A:                    2.4.52

### Flag 28

Enumerate users on the machine at 10.10.1.22 using Enum4linux and find the relative identifier (RID) for the user “shiela.”

{% code title="Parrot Terminal" %}

```bash
enum4linux -u martin -p apple -U 10.10.1.22
```

{% endcode %}

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-23.bmp" alt="" height="350" width="386"><figcaption></figcaption></figure>

A:                    0x451

### Flag 29

Enumerate the machine at 10.10.1.22 using Enum4linux and find its Platform\_ID.

{% code title="Parrot Terminal" %}

```bash
enum4linux -u martin -p apple -O 10.10.1.22
```

{% endcode %}

Try:                 enum4linux -u martin -p apple -0 10.10.1.22

<figure><img src="https://blogalpharhob.com/wp-content/uploads/2023/02/Image-24.bmp" alt="" height="170" width="624"><figcaption></figcaption></figure>

A:                    500

### Flag 30

Enumerate the machine at 10.10.1.22 using Enum4linux and find its server type.

From the previous code.

A:                    0x84102f